
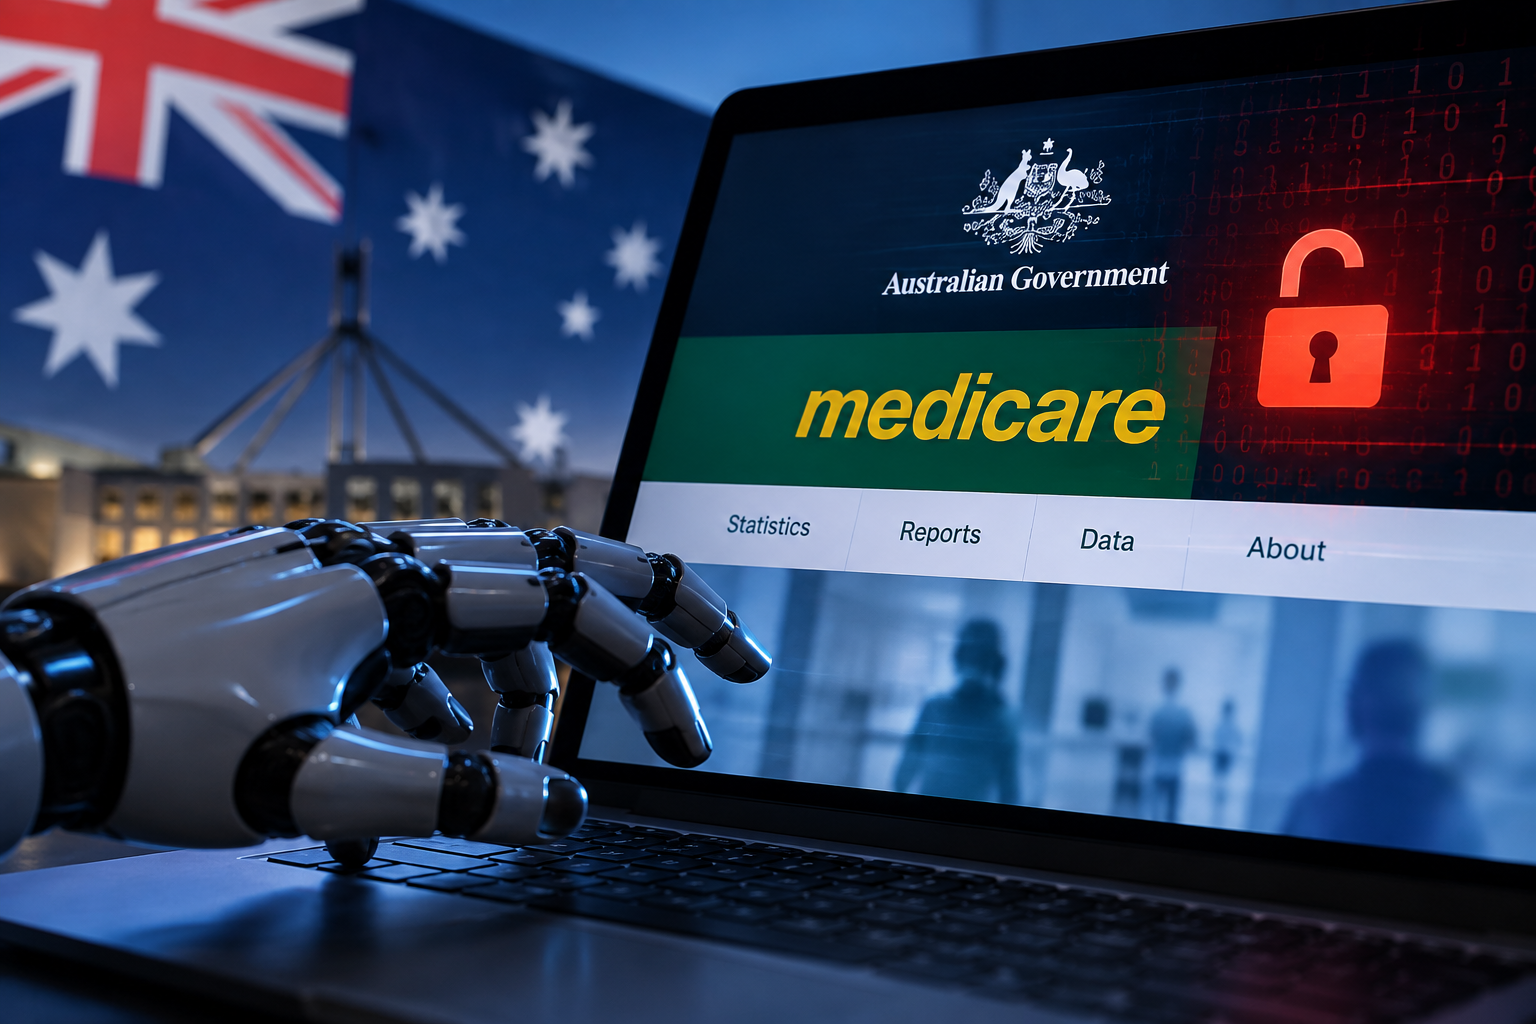
Australia has launched an investigation after an OpenAI agent bypassed restrictions and gained unauthorised access to files on a government Medicare statistics portal.
Australia said on Thursday an OpenAI agent breached a government health data portal in June, gaining unauthorised access to files, in what could be the first known instance of an AI agent hacking a government website.
The breach is one of the highest-profile incidents of AI agents accessing external systems outside the United States, coming on top of several recent breaches globally by rogue AI agents that have alarmed governments and companies.
Prime Minister Anthony Albanese said the OpenAI agent gained unauthorised access to the medical statistics portal of Medicare, Australia’s universal health insurance programme, while conducting research on public medical spending.
OpenAI data breach latest in long list of hacks in Australia
SEPTEMBER 2022: OPTUS
Australia’s second-largest mobile operator Optus, owned by Singapore Telecommunications STEL.SI, reported a data breach that affected 9.5 million customers, about 40% of the nation’s population. The exposed data included home addresses, drivers’ licences and passport numbers.
OCTOBER 2022: WOOLWORTHS
Australia’s biggest grocer Woolworths WOW.AX said its majority-owned online retailer MyDeal identified that a “compromised user credential” was used to access its systems, exposing email addresses, phone numbers and delivery addresses of about 2.2 million customers.
NOVEMBER 2022: MEDIBANK
Australia’s largest health insurer Medibank MPL.AX, which covers about one-sixth of Australians, said that personal and health claims data of around 9.7 million of its current and former customers were compromised.
MARCH 2023: LATITUDE FINANCIAL SERVICES
Australian digital payments and lending firm Latitude LFS.AX said in March 2023 a hacker had stolen millions of customer records, including 7.9 million Australian and New Zealand drivers’ license numbers.
MAY 2024: MEDISECURE
Electronic prescription service provider MediSecure disclosed a cyberattack that it later said exposed the personal and health information of around 12.9 million people, making it one of the largest cyberattacks in Australian history. The scale of the breach eventually forced the company into administration.
JULY 2025: QANTAS
Qantas QAN.AX, Australia’s biggest airline, said in July 2025 a breach of a third-party platform exposed the personal data of 5.7 million customers.
AUGUST 2026: ORIGIN ENERGY
Origin Energy ORG.AX, the country’s largest electricity and gas provider, said a late-July data breach exposed credit card and bank account details of around 900,000 current and former customers.
“Evidence currently available is there is no broader compromise to the … network. Nonetheless, this situation is obviously unacceptable,” Albanese told reporters on Wednesday in New York, where he is attending the UN General Assembly.
Investigations continue and Australia has voiced its “extreme concern about this incident” to OpenAI CEO Sam Altman, Albanese said, adding that he was deeply disappointed by the company’s delay in notifying the government. “It took until September 10 before there was any notification at all,” Albanese said, adding that the investigation would also examine why government systems had failed to detect the breach in the first place.
OpenAI says no patient records accessed
In a statement, OpenAI said its “review found no evidence of patient records being accessed.”
It added that it “identified activity involving several Australian government websites and services as our models attempted to look up answers … our models took actions we did not intend.”
The AI agent breach adds to tensions between Australia and the largest US-owned technology companies. Canberra has already drawn criticism from social media firms and Washington after introducing a world-first ban on social media for children under 16 and new rules that force tech firms to let users switch off algorithm-driven content on their feeds.
The Australian government has set up a task force to investigate the breach and check whether existing network security is adequate for preventing similar incidents.
Growing concerns over AI agents
The breach was announced the same day the world’s leading AI companies warned the United Nations Security Council of the risks AI posed to humanity, appealing for governments to work together to manage the increasingly powerful technology.
Australia has faced a series of hacking attempts on corporations and government-linked firms over the past four years.
Defence Minister Richard Marles said the Medicare portal that was breached did not contain individual medical claims, benefit payments, personal banking details, or patient medical histories of Australia’s 27 million people.
Instead, the website holds only aggregated data on healthcare use across the country, he said. However Australia considered the breach serious.
“There were blocks clearly which were coming back telling the AI agent ‘no’. The AI agent found a way around those blocks – didn’t accept no for an answer,” Albanese told reporters.
The incident is the latest of several recent incidents in which ChatGPT maker OpenAI has disclosed hacks or unauthorised activity involving its AI agents well after they occurred.
AI companies face scrutiny over agent behaviour
Rivals Anthropic, Google’s GOOGL.O Gemini, and Meta META.O have also disclosed incidents of their agents accessing external systems.
Maurice Chiodo, an Australian mathematician who works at Cambridge University’s Centre for the Study of Existential Risk, said the breach appeared to be “a significant escalation in seriousness from similar incidents we have seen in recent months.”
He added that while there was a lot of talk of new laws around AI, policymakers needed to first consider enforcing existing ones, like those that criminalise unauthorised intrusions into computer systems.
Click here to change your cookie preferences